Hackers Exploit OpenSSH Flaw Within Hours
Tap title to read story
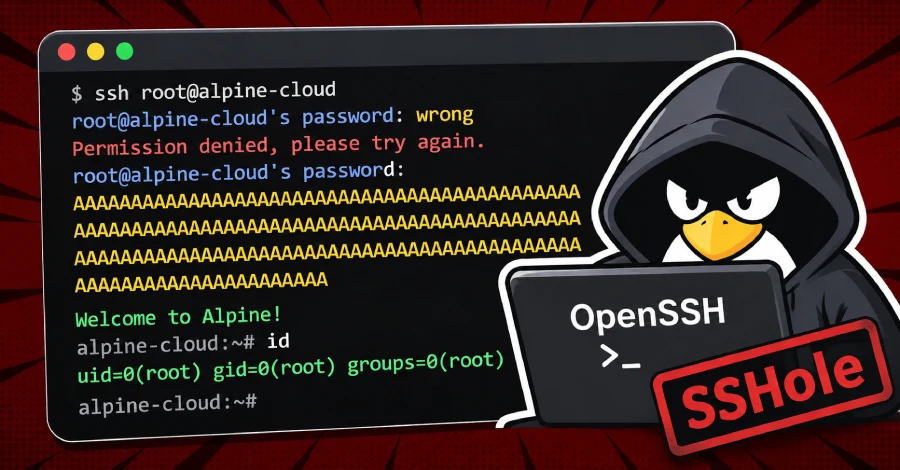
Attackers have exploited a newly disclosed OpenSSH vulnerability, CVE-2026-123158, within hours of its public announcement. The flaw, codenamed SSHole, allows unauthenticated users to supply oversized passwords and gain access to accounts that have no usable password set on systems using the musl C library with PAM disabled, such as Alpine Linux. An attacker can use a password between two hundred fifty-seven and one thousand twenty‑four bytes to trigger a hash failure that returns an asterisk, matching the stored hash and granting login. The issue traces back to a 2016 patch for a username‑enumeration bug. OpenSSH 10.6p2 now fixes the flaw, and root access was confirmed on a honeypot.
More context
Timeline
- On November 4 2026 OpenSSH 10.6p2 released, patching the SSHole vulnerability.
Why it matters
Immediate US impact: Rapid exploitation threatens critical infrastructure servers and may enable lateral movement. Possible long-term US impact: Future updates required for all musl-based Linux distributions. Most affected groups: System administrators managing Alpine Linux servers and other musl-based deployments. Reader priority: Users should apply the 10.6p2 patch immediately to prevent unauthorized access.
Coverage notes
Center: Coverage from openssh.org, sepe.gr, osintsights.com frames this as a developing news story: Hackers Exploit OpenSSH Flaw Within Hours. Reporting emphasizes verified facts, named sources, and near-term impact for readers. Left: Left-leaning desks covering the same development typically emphasize public impact, institutional accountability, and who is most affected. Right: Right-leaning desks covering the same development typically emphasize practical outcomes, market or security stakes, and institutional response.
Primary report
The Hacker News — Hackers Exploit OpenSSH Flaw Within Hours
Sources
- malwarebytes.com
- npr.org
- nbcnews.com
- openssh.org
- sepe.gr
- osintsights.com
- maketecheasier.com
- pcgamer.com
- cyberpolicy.com
- execsecurity.com
- techradar.com
- undercodenews.com
- imdb.com
- riskaware.io
- cpomagazine.com
- cybernews.com
- proofpoint.com
- advisory.eventussecurity.com
- cybernoz.com
- gbhackers.com
- securityboulevard.com
- bellatorcyber.com
- bleepingcomputer.com
- cyberdefensemagazine.com
- siteguarding.com
- nytimes.com
- rewterz.com
- pcrisk.com
- bloomberg.com
- cybersecuritynews.com
- learnonlinesecurity.com
- etsitsolutions.com
- cyberpress.org
- infosecurity-magazine.com
- thehackernews.com
- cinteot.com
- huntress.com
- blog.gitguardian.com
- wired.com
- analyticsinsight.net
- privacybee.com
- pcmag.com
- tunedsecurity.com
- frameworksecurity.com
- csoonline.com
- zdnet.com
- en.wikipedia.org
- ssh.com
- fastcompany.com
- The Hacker News
JQJO Editorial Desk · Human reviewed · AI assisted. Report a correction.