PHP2Shell Exploits Confirmed in Wild
Tap title to read story
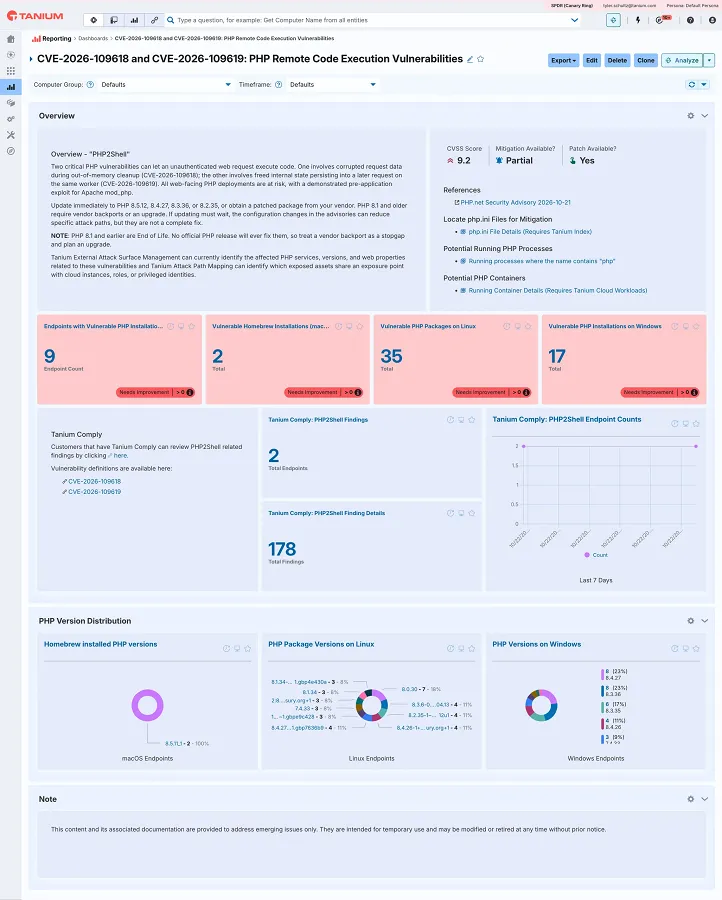
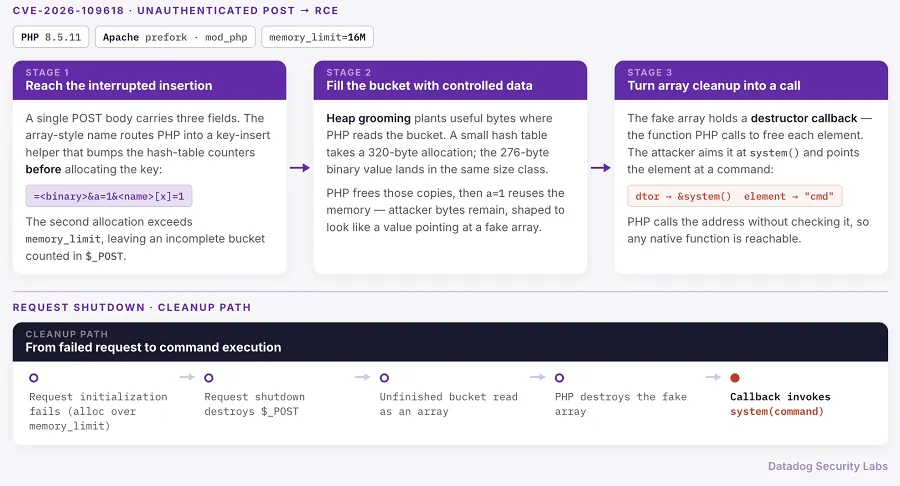
Two critical RCE vulnerabilities, CVE‑2026‑109618 and CVE‑2026‑109619, collectively known as PHP2Shell, have been successfully exploited in the wild.
The malicious activity was captured by Adel Karimi, detection and response lead at Perplexity, whose honeypots recorded confirmed remote code execution against an Apache mod_php installation running PHP 8.4.26.
Karimi reported an 800 KiB decoded cookie dump and a function address derived from that dump, with the shell command executing about 1.6 ms after the final captured byte.
Marcus Hutchins of Expel confirmed the findings and praised the technical detail.
The PHP security team patched the flaws on Wednesday, October 21, one day after urging admins to install the updates.
Multiple cybersecurity firms, including Cloudflare, Hadrian, watchTowr, Previdian, and Patchstack, detected exploitation attempts before public disclosure but flagged them as unsuccessful.
More context
Timeline
- On October 21 2026 PHP security team patches PHP2Shell vulnerabilities.
Why it matters
Immediate US impact: Potential compromise of PHP‑based web services nationwide Possible long-term US impact: Increased scrutiny of PHP security updates Most affected groups: Web developers and hosting providers Reader priority: Understand immediate patch requirements
Coverage notes
Center: Coverage from wiz.io, recordedfuture.com, en.wikipedia.org frames this as a developing news story: PHP2Shell Exploits Confirmed in Wild. Reporting emphasizes verified facts, named sources, and near-term impact for readers. Left: Left-leaning desks covering the same development typically emphasize public impact, institutional accountability, and who is most affected. Right: Right-leaning desks covering the same development typically emphasize practical outcomes, market or security stakes, and institutional response.
Primary report
BleepingComputer — PHP2Shell Exploits Confirmed in Wild
Sources
JQJO Editorial Desk · Human reviewed · AI assisted. Report a correction.