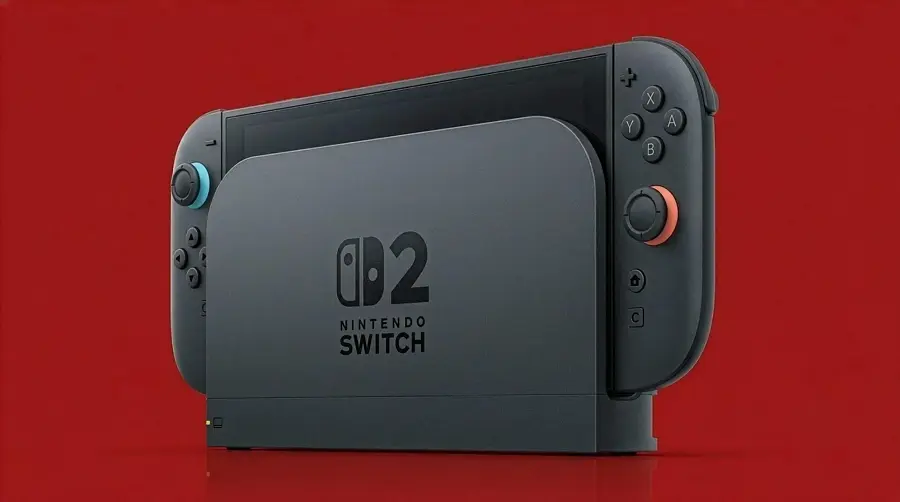
Switch 2 Jailbreak Exposes Homebrew Vulnerability
Tap title to read story
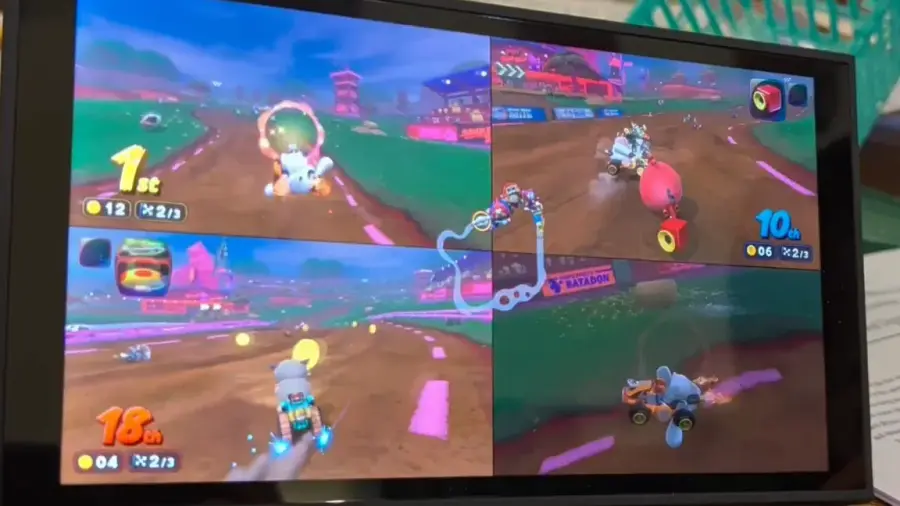
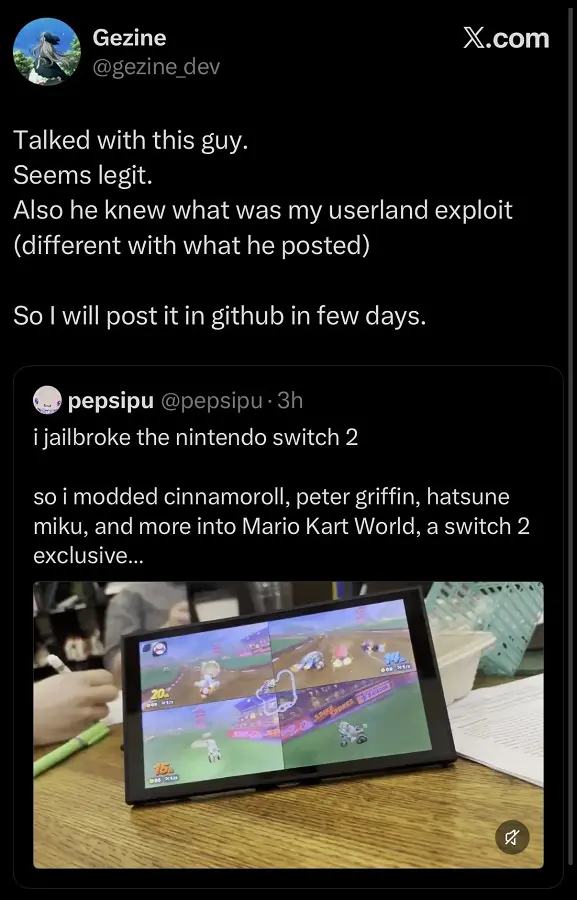
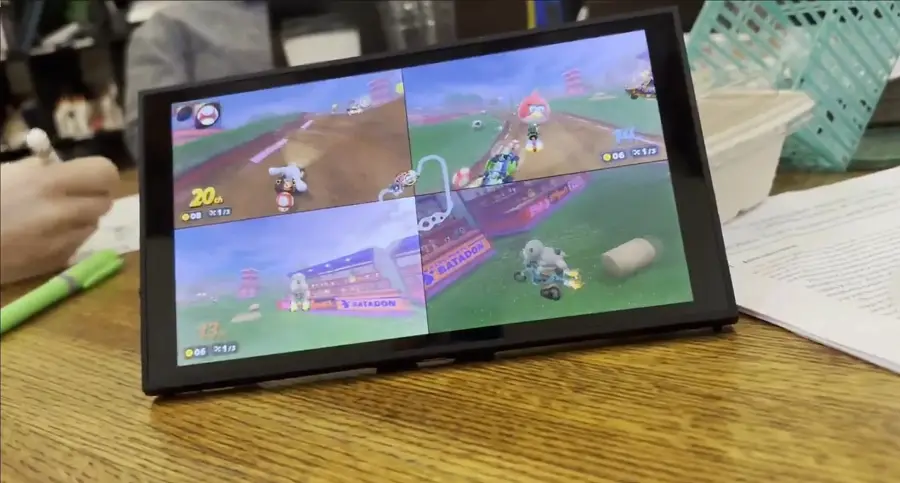
A security researcher demonstrated a software‑only jailbreak of the Switch 2, gaining userland access that allows running homebrew, backing up save files, and accessing most peripherals. The exploit relies on an integer overflow in the original Switch version of SmileBasic 4, a programming environment previously used in the 3DS smilehax hack. After about two weeks of testing, the researcher discovered a 32‑bit overflow that exposes an array pointer, enabling read/write access to system memory. From there, a buffer overflow in the FileSystem services module granted arbitrary read/write privileges, leading to native code execution. The proof‑of‑concept included modded characters in Mario Kart World, but the current userland exploit remains sandboxed and does not provide kernel‑level control.
More context
Timeline
- On March 3 2017 Nintendo Switch released worldwide.
- On June 8 2025 First Switch 2 jailbreak discovered.
Coverage notes
Center: Coverage from Ars Technica frames this as a developing news story: Switch 2 Jailbreak Exposes Homebrew Vulnerability. Reporting emphasizes verified facts, named sources, and near-term impact for readers. Left: Left-leaning desks covering the same development typically emphasize public impact, institutional accountability, and who is most affected. Right: Right-leaning desks covering the same development typically emphasize practical outcomes, market or security stakes, and institutional response.
Primary report
Ars Technica — Switch 2 Jailbreak Exposes Homebrew Vulnerability
Sources
JQJO Editorial Desk · Human reviewed · AI assisted. Report a correction.