Switch 2 越狱暴露自制漏洞
Tap title to read story
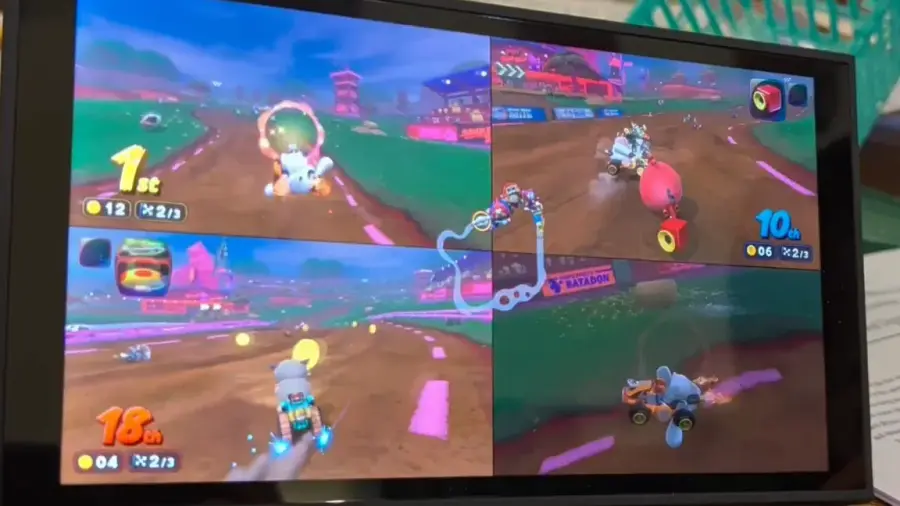
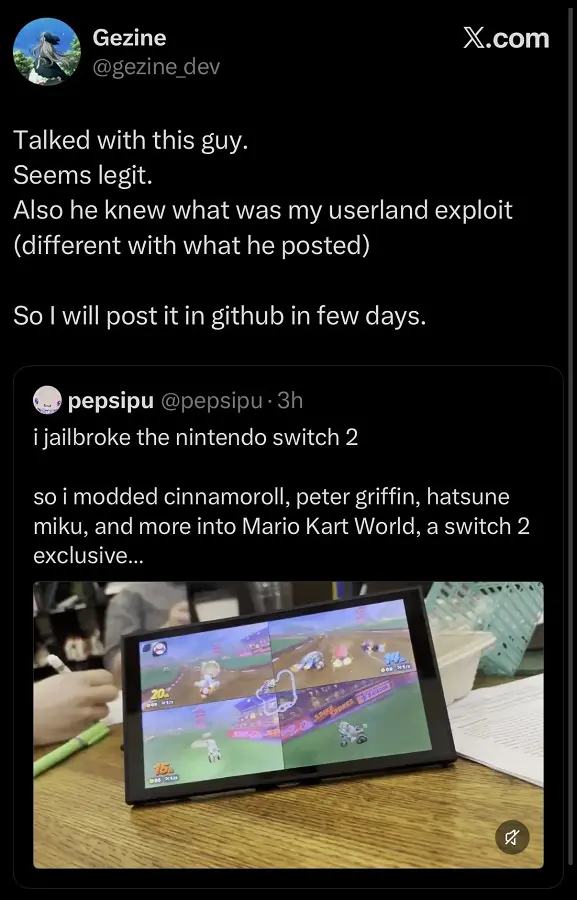
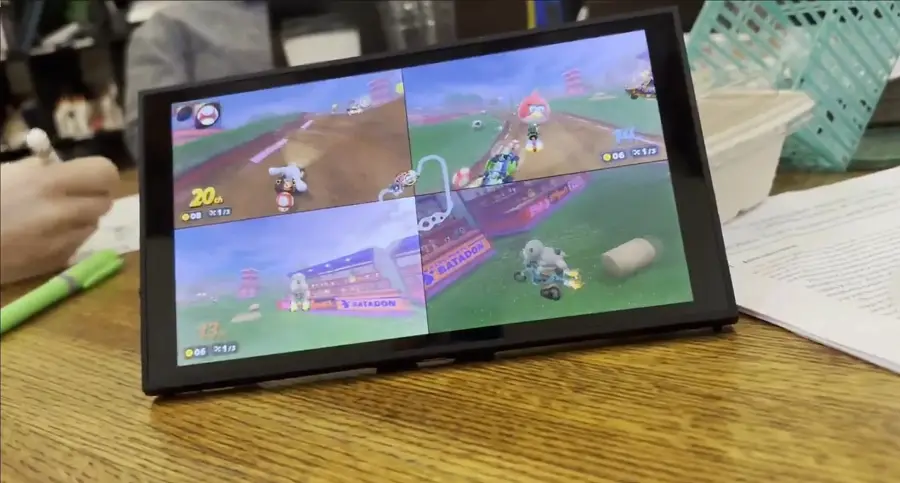
一位安全研究人员演示了 Switch 2 的纯软件越狱,获得了允许运行自制程序、备份存档文件以及访问大多数外围设备的 userland 访问权限。此漏洞利用了 SmileBasic 4 的原始 Switch 版本中的整数溢出,SmileBasic 4 是之前在 3DS smilehax 攻击中使用的编程环境。经过大约两周的测试,研究人员发现了一个 32 位溢出,该溢出暴露了一个数组指针,从而能够对系统内存进行读写访问。随后,FileSystem 服务模块中的缓冲区溢出授予了任意读写权限,从而实现了原生代码执行。概念验证包括《马力欧卡丁车 8 豪华版》中的修改角色,但当前的 userland 漏洞利用仍然被沙盒化,并且不提供内核级控制。
More context
Timeline
- On March 3 2017 Nintendo Switch released worldwide.
- On June 8 2025 First Switch 2 jailbreak discovered.
Coverage notes
Center: Coverage from Ars Technica frames this as a developing news story: Switch 2 Jailbreak Exposes Homebrew Vulnerability. Reporting emphasizes verified facts, named sources, and near-term impact for readers. Left: Left-leaning desks covering the same development typically emphasize public impact, institutional accountability, and who is most affected. Right: Right-leaning desks covering the same development typically emphasize practical outcomes, market or security stakes, and institutional response.
Primary report
Ars Technica — Switch 2 Jailbreak Exposes Homebrew Vulnerability
Sources
JQJO Editorial Desk · Human reviewed · AI assisted. Report a correction.