PHP Vulnerabilities Leaked Ahead of Scheduled Patch Release
Tap title to read story
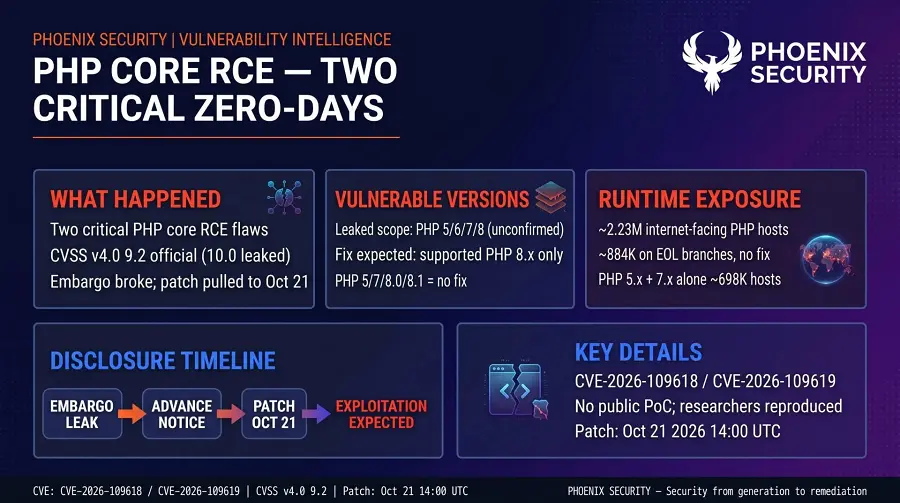
Two critical PHP remote‑code‑execution flaws, CVE‑2026‑109618 and CVE‑2026‑109619, were disclosed on the Hacker News forum on October 20, a day before the PHP security team’s planned public disclosure and patch release at 2 pm GMT on October 21. The leaks, attributed to user ‘petecooper’, revealed the CVE identifiers and claimed the vulnerabilities would be disclosed on October 22. The PHP team confirmed the patches would be released on October 21 and assigned a CVSS score of 9.2, lower than the maximum 10.0 suggested by the leak. CERT‑EU and the UK NCSC issued emergency advisories urging users to prepare for remediation. PHP powers roughly 69.7 % of websites that use a server‑side language, including WordPress, Drupal, Joomla and Magento. The premature leak could enable attackers to exploit the flaws before patches are available.
More context
Timeline
- On October 20 2026 User leaks PHP vulnerability identifiers on Hacker News forum.
- On October 20 2026 PHP security team confirms scheduled disclosure on October twenty‑first.
- On October 21 2026 CERT‑EU releases emergency advisory for PHP vulnerabilities.
- On October 21 2026 PHP releases patches for CVE‑2026‑109618 and CVE‑2026‑109619.
Why it matters
Immediate US impact: Urgent patching required for PHP‑based web services. Possible long-term US impact: Increased vigilance for early vulnerability disclosure. Most affected groups: Web developers, CMS administrators, e‑commerce platforms. Reader priority: Apply patches immediately to prevent exploitation.
Coverage notes
Center: Coverage from cert.europa.eu, Help Net Security, Rescana frames this as a developing news story: PHP Vulnerabilities Leaked Ahead of Scheduled Patch Release. Reporting emphasizes verified facts, named sources, and near-term impact for readers. Left: Left-leaning desks covering the same development typically emphasize public impact, institutional accountability, and who is most affected. Right: Right-leaning desks covering the same development typically emphasize practical outcomes, market or security stakes, and institutional response.
Primary report
Infosecurity Magazine — PHP Vulnerabilities Leaked Ahead of Scheduled Patch Release
Sources
JQJO Editorial Desk · Human reviewed · AI assisted. Report a correction.