AI Coding Assistant Hijacked to Spread Worm Across 100 Repositories
PUBLISHED Sep 16, 2026, 10:48 AM ET
Read, Watch or Listen
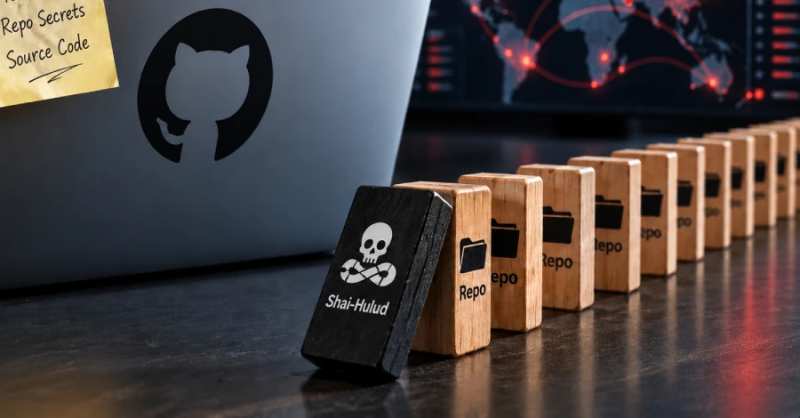
Mandiant reported a significant cybersecurity incident involving an artificial intelligence coding assistant at an undisclosed software provider. In September 2026, an attacker compromised an active developer session after poisoning recommended software packages. This flaw allowed the unauthorized installation of an infostealer via a malicious PyPI package, alongside the theft of GitHub OAuth tokens and repository secrets. Leveraging these stolen credentials and active session permissions, the threat actor deployed the automated Shai Hulud worm across approximately one hundred internal code repositories. This breach exposed proprietary source code and corporate assets, demonstrating a rising threat vector where automated developer workflows and AI coding tools are directly weaponized against enterprise software supply chains. Security analysts emphasize that organizations must implement stricter validation checks on automated code suggestions, secure developer authentication sessions, and monitor repository access continuously to prevent similar widespread internal compromises from paralyzing sensitive corporate infrastructure across the global enterprise software sector.
By Shahbaz A. | JQJO News
Timeline of Events
- On September 1, 2026: Attackers poisoned various software repository packages.
- On September 5, 2026: Developers accepted compromised coding assistant recommendations.
- On September 8, 2026: Infostealer malware successfully installed on systems.
- On September 10, 2026: Threat actors stole GitHub OAuth tokens.
- On September 12, 2026: Unauthorized access permissions enabled internal compromise.
- On September 14, 2026: Malicious worm deployed across code repositories.
- On September 15, 2026: Mandiant investigators detected unusual repository activity.
- On September 16, 2026: Security advisory detailing assistant hijacking published.
- On September 17, 2026: Affected organizations revoked compromised tokens immediately.
- On September 18, 2026: Industry experts predict stricter AI governance.
News Intelligence
- Immediate US impact: Enterprise software firms face heightened supply chain security threats nationwide.
- Possible long-term US impact: Stricter regulations will govern artificial intelligence coding assistants moving forward.
- Most affected groups: Software developers, enterprise security teams, and major technology corporations nationwide.
- Reader priority: Monitor repository access logs and carefully verify automated code recommendations.
- Articles Published:
- 20
- Right Leaning:
- 1
- Left Leaning:
- 1
- Neutral:
- 18
- Distribution:
- Left 5%, Center 90%, Right 5%
Left: Highlights corporate security failures and urges stricter artificial intelligence regulations. Center: Reports technical details regarding Mandiant disclosure without taking political sides. Right: Emphasizes free market risks and software vulnerabilities within automated tools.
Mandiant disclosed coding assistant hijacking spreading worm across code repositories. https://thehackernews.com/2026/09/attacker-hijacks-ai-coding-assistant.html
Coverage of Story:
From Left
Why the latest AI software supply chain hack changes everything for developers
Fast CompanyFrom Center
Attacker Hijacks AI Coding Assistant to Spread Worm Across 100 Repositories
The Hacker News Zscaler Mend.io Cloud Security Alliance Dark Reading Reuters Bloomberg Wall Street Journal Financial Times PCMag IT Pro Today The Register VentureBeat Axios Politico Tech Google Cloud Blog DarkReading Extra Security Boulevard

Comments