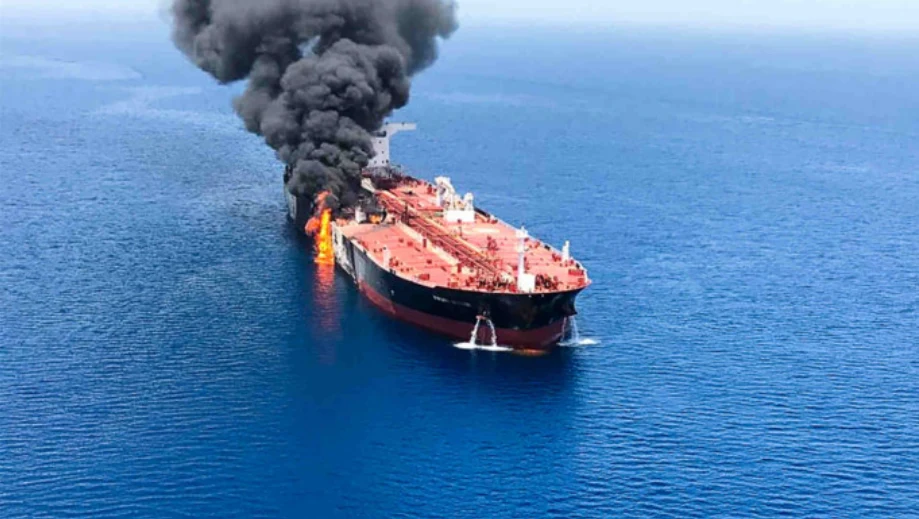
U.S. Probes Cyberattacks on Energy Tankers Bound for American Coast
Tap title to read story
United States federal authorities have launched a formal investigation into cyberattacks targeting foreign energy tankers bound for American ports. The Federal Bureau of Investigation and the U.S. Coast Guard initiated probes after digital intrusions were detected on commercial vessels transporting oil and liquefied natural gas. Investigators boarded and inspected vessels, including the Liberian-flagged oil tanker VL Prosperity near Galveston, Texas, following network disruptions. Security reports indicated the vessel previously experienced a 30-hour communications blackout during transit near the Strait of Gibraltar, which impacted engine-room monitoring systems and fuel controls. Federal officials are examining whether foreign state-sponsored actors are utilizing advanced cyber warfare techniques to disrupt critical maritime supply chains and energy imports. The Department of Homeland Security is coordinating with international shipping companies to enhance cybersecurity protocols across vessels operating near United States territorial boundaries. No casualties, environmental spills, or immediate operational disruptions have been reported by officials during the ongoing investigation.
More context
Timeline
- On August 7, 2026, the oil tanker VL Prosperity experienced a communications blackout during transit.
- On August 20, 2026, Iran's Mehr News Agency reported on the vessel's communications outage.
- On August 21, 2026, U.S. Coast Guard and FBI teams boarded the vessel to investigate.
- On August 24, 2026, Iranian state media published commentary regarding maritime cybersecurity vulnerabilities.
- On September 14, 2026, the U.S. Coast Guard established a new Office of Maritime Cybersecurity Policy.
- On September 15, 2026, the U.S. Coast Guard officially confirmed the ongoing federal cyberattack investigations.
- On September 16, 2026, major financial and news outlets reported extensive details on the tanker probes.
- On September 16, 2026, maritime stakeholders coordinated with federal agencies to secure commercial vessel networks.
- In coming months, federal authorities expect to issue enhanced cybersecurity mandates for inbound commercial shipping fleets.
- In coming years, maritime regulators plan to deploy advanced threat detection systems across major U.S. ports.
Why it matters
Immediate US impact: Federal probe heightens domestic vigilance over critical maritime energy infrastructure. Possible long-term US impact: Expanded cybersecurity protocols will permanently alter global commercial shipping security standards. Most affected groups: Mainly affects commercial ship operators, energy importers, and federal security agencies. Prioritize Updates: Prioritize updates from official Coast Guard advisories and verified maritime wire reports.
Coverage notes
Left: Framing emphasizes national security vulnerabilities and foreign state-sponsored digital threats. Center: Framing focuses strictly on factual agency confirmations and maritime security operations. Right: Framing highlights potential foreign adversaries and risks to domestic energy infrastructure.
Primary report
U.S. Coast Guard and FBI confirmed cyberattack investigations on September 15, 2026.
Sources
JQJO Editorial Desk · Human reviewed · AI assisted. Report a correction.