Microsoft Fixes Record 964 Flaws on Patch Tuesday, Including Two Actively Exploited Zero-Days
Tap title to read story
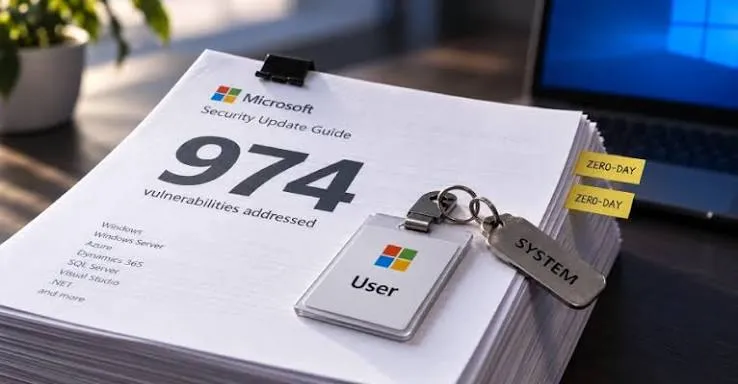
Microsoft released its largest security update on record for September 2026, addressing 964 vulnerabilities across enterprise software and core Windows components. The massive rollout includes 104 critical flaws and 860 important issues affecting products such as Exchange Server, SharePoint, SQL Server, and Microsoft Office. Most notably, the update patches two actively exploited zero-day vulnerabilities tracked as CVE-2026-81963 and CVE-2026-85880. Both carry a CVSS severity score of 7.8 out of 10 and allow local attackers who already possess device access to elevate privileges to SYSTEM level. The first flaw involves improper link resolution within the Windows Update Stack, while the second is a heap-based buffer overflow in the Advanced Local Procedure Call messaging system enabling sandbox escapes. Security agencies urge immediate administrator deployment. The release coincides with heightened cybersecurity alerts regarding industrial model distillation by foreign actors.
More context
Timeline
- On September 8 2026 Agencies issued joint advisory regarding industrial AI model distillation.
- On September 8 2026 Security researchers detected active exploitation of local elevation zero days.
- On September 9 2026 Microsoft published security updates addressing 964 active customer vulnerabilities.
- On September 9 2026 Security analysts began evaluating windows update stack heap overflow flaws.
- On September 9 2026 Enterprise administrators initiated emergency patching protocols across global server infrastructure.
- On September 9 2026 Cybersecurity firms confirmed active exploitation details regarding heap buffer overflows.
- On September 10 2026 Administrators will complete preliminary deployment testing for critical exchange servers.
- On September 15 2026 Organizations expect full remediation across non-critical workstation deployments worldwide.
- On October 9 2026 Routine telemetry reports will measure initial corporate patching compliance rates.
- On November 9 2026 Secondary threat actor exploitation attempts are anticipated against unpatched systems.
Why it matters
Immediate US impact: Organizations face immediate exploitation risks requiring urgent administrative patch deployments. Possible long-term US impact: Unpatched enterprise servers risk long term persistent network compromise vectors. Most affected groups: Enterprise system administrators managing windows infrastructure across united states enterprises. Reader priority: Prioritize official security advisories over speculative social media commentary.
Coverage notes
Left: Highlighted systemic corporate software quality failures and regulatory oversight needs. Center: Reported factual technical details regarding vulnerability counts and zero day specifics. Right: Emphasized national security implications and threats from foreign adversarial actors.
Primary report
Microsoft published September 2026 security update bulletin on September 9 2026.
Sources
- Malwarebytes
- Tenable
- CSO Online
- Gadget Hacks
- CrowdStrike
- Dark Reading
- Baidu Security
- AliSec
- Qihoo 360 Netlab
- 腾讯安全应急响应中心
- Anhui Security
- SecNews
- PCMag
- Forbes
- IT Pro Today
- VentureBeat
- Krebs on Security
- SANS Internet Storm Center
- Action1 Blog
- Kaspersky Daily
- Sophos News
- IBM X-Force Exchange
- Mandiant Threat Intelligence
- Microsoft Security Response Center
- CISA Current Activity
JQJO Editorial Desk · Human reviewed · AI assisted. Report a correction.