ShinyHunters Hacks Pharmaceutical Giant McKesson
Tap title to read story
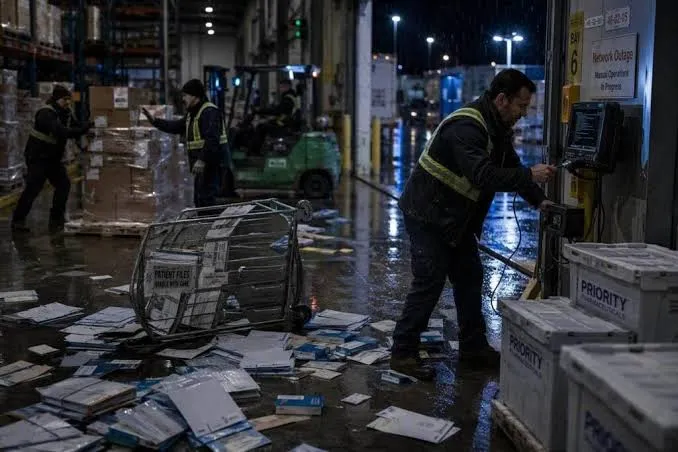
Pharmaceutical distributor McKesson confirmed it is investigating a major cybersecurity incident and data breach after the extortion group ShinyHunters claimed responsibility. McKesson Chief Technology Officer Francisco Fraga announced the intrusion affected an unnamed third-party application environment, prompting unauthorized data exfiltration. Unlike standard containment protocols that instantly disconnect entire networks, the corporation chose not to proactively sever core infrastructure systems. Customers across the United States reported intermittent service degradation affecting supply chains, order processing, and distribution networks. McKesson filed formal regulatory disclosures with the U.S. Securities and Exchange Commission regarding the breach. The incident follows similar cyberattacks targeting major medical infrastructure corporations, including Boston Scientific, Medtronic, and Stryker. Federal law enforcement agencies previously warned companies about extensive extortion campaigns orchestrated by ShinyHunters targeting cloud environments. The investigation remains active as federal authorities and cybersecurity specialists examine the scope of the compromised third-party environment and evaluate potential data leaks.
More context
Timeline
- On August 30 2026 ShinyHunters publicly claimed responsibility for the McKesson cyberattack.
- On August 31 2026 McKesson confirmed investigating a major cybersecurity incident today.
- On August 31 2026 CTO Francisco Fraga announced third-party application environment intrusion.
- On August 31 2026 Customers reported intermittent supply chain and order processing degradation.
- On August 31 2026 McKesson filed formal regulatory disclosures with the SEC today.
- On August 31 2026 Federal law enforcement warned about ongoing cloud extortion campaigns.
- On September 1 2026 Investigators will analyze affected third-party application environment security logs.
- On September 5 2026 Regulatory authorities expect comprehensive incident impact reports from McKesson.
- On October 15 2026 Federal agencies anticipate releasing updated healthcare sector cybersecurity advisories.
- On November 30 2026 Affected supply chain networks expect full operational service restoration.
Why it matters
Immediate US impact: Intermittent healthcare supply chain disruptions affect nationwide distribution networks. Possible long-term US impact: Heightened regulatory scrutiny on third-party cloud software vendor security. Most affected groups: Pharmaceutical distributors, healthcare providers, and federal law enforcement agencies. Reader priority: Monitor verified regulatory filings and official corporate security updates closely.
Coverage notes
Left: Emphasizes corporate regulatory accountability and third-party software vendor vulnerabilities. Center: Reports official statements, operational supply chain impacts, and regulatory filings. Right: Focuses on federal law enforcement warnings and critical infrastructure security.
Primary report
McKesson confirmed investigating a major cybersecurity incident on August 31, 2026.
Sources
- Reuters
- Associated Press
- Bloomberg
- Wall Street Journal
- CNBC
- TechCrunch
- BleepingComputer
- Dark Reading
- CyberScoop
- SecurityWeek
- ZDNet
- The Record by Recorded Future
- Forbes
- Reuters Legal
- Fierce Healthcare
- Modern Healthcare
- Becker's Hospital Review
- Healthcare Dive
- SC Media
- Infosecurity Magazine
- Help Net Security
- The Hill
- Politico
- Washington Post
- New York Times
- Los Angeles Times
- USA Today
- Axios
- CISA Advisory
- HHS HC3
- SEC EDGAR
- Reuters Breakingviews
- Financial Times
- San Francisco Chronicle
- Dallas Morning News
- Atlanta Journal-Constitution
- MedCity News
- PharmaVoice
- Supply Chain Dive
JQJO Editorial Desk · Human reviewed · AI assisted. Report a correction.