ATF Investigating Major Cybersecurity Incident Amid Qilin Ransomware Claims
Tap title to read story
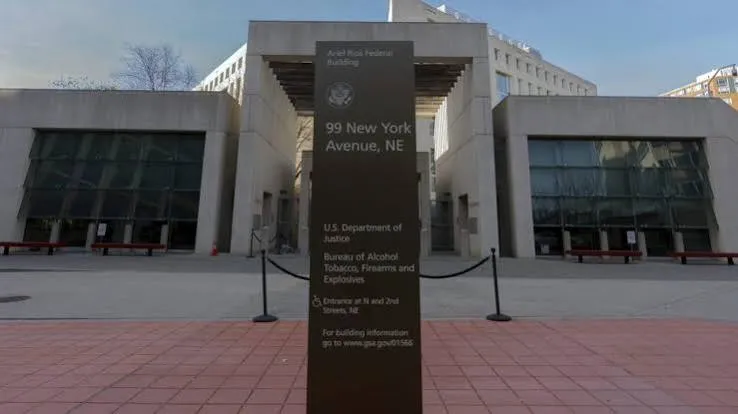
The Bureau of Alcohol, Tobacco, Firearms and Explosives confirmed Wednesday it is investigating a major cybersecurity incident after the Russian-linked Qilin ransomware group claimed responsibility on its dark web site. Senior Department of Justice officials classified the event as a major incident under federal guidelines. The ATF stated that a standalone system operating separately from the main enterprise network was affected. Agency officials emphasized that critical platforms, including the eForms system, do not appear compromised. Connections to the affected environment were immediately terminated to initiate forensic investigations and incident response procedures. The agency has not yet confirmed Qilin's involvement, the exact timeline of the intrusion, or whether data was exfiltrated. The Qilin syndicate is known for aggressive double-extortion tactics involving stolen data leaks. Federal law enforcement agencies continue assessing the broader implications of the intrusion while maintaining operational security across essential regulatory networks.
More context
Timeline
- On 2022-03-01 The Russian-linked Qilin ransomware group launched initial cyberattacks.
- On 2026-02-23 CyberNews reported Qilin listed ATF on dark web.
- On 2026-02-25 ATF confirmed investigating a major federal cybersecurity incident.
- On 2026-02-25 Department of Justice designated the breach a major incident.
- On 2026-02-25 ATF disconnected affected standalone systems from enterprise network.
- On 2026-02-25 Agency officials verified critical eForms systems remained uncompromised.
- On 2026-02-26 Forensics teams initiated comprehensive data exfiltration and compromise analysis.
- On 2026-02-26 Investigators will determine scope of potential data theft.
- On 2026-03-05 Federal agencies will release detailed post-incident forensic findings.
- On 2026-04-01 Congress may convene oversight hearings regarding federal cybersecurity defenses.
Why it matters
Immediate US impact: Federal networks face heightened scrutiny following ransomware infiltration threats. Possible long-term US impact: Federal agencies will strengthen standalone network isolation and monitoring. Most affected groups: Bureau of Alcohol, Tobacco, Firearms and Explosives federal investigators. Reader priority: Verify official Department of Justice statements over unconfirmed dark web.
Coverage notes
Left: Highlighted federal vulnerabilities, systemic risks, and foreign adversary threats. Center: Focused strictly on official statements, agency containment, and verified facts. Right: Emphasized federal security failures and potential law enforcement operational impacts.
Primary report
ATF announced investigation into cybersecurity incident on February 25, 2026.
Sources
- NBC News
- Washington Post
- Vice Motherboard
- CyberNews
- The Record
- SecurityWeek
- BleepingComputer
- Dark Reading
- CyberScoop
- InfoSecurity Magazine
- The Hacker News
- SC Media
- TechCrunch
- Reuters
- Associated Press
- Bloomberg
- CNN
- CBS News
- ABC News
- Wall Street Journal
- Politico
- The Hill
- Axios
- Ars Technica
- The Register
- Forbes
- Fortune
- Wired
- ZDNET
- Fox News
JQJO Editorial Desk · Human reviewed · AI assisted. Report a correction.