T-Mobile Cuts Network Cable to Stop Chinese State-Backed Hackers
Tap title to read story
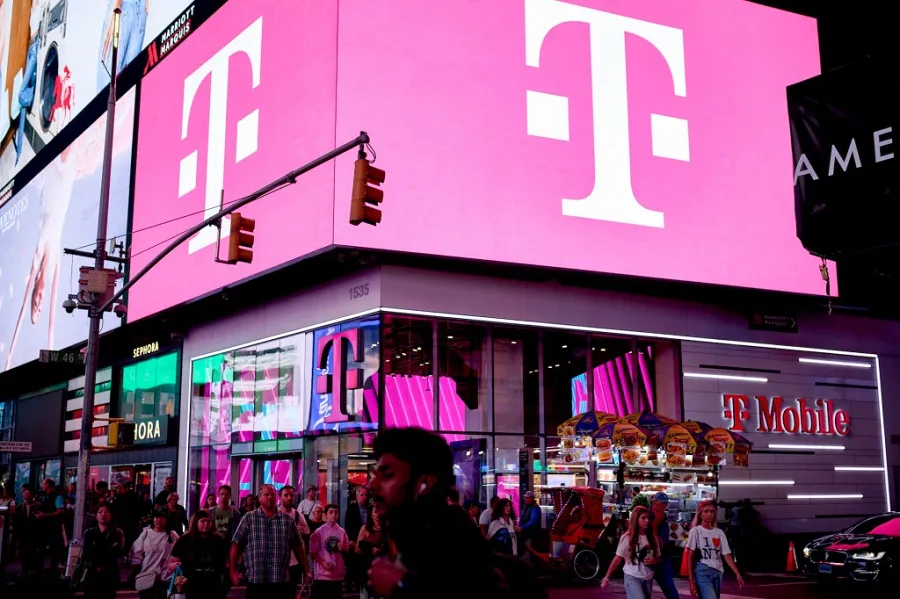
T-Mobile’s security team physically severed a network cable in 2024 after tracing suspicious activity to a router operated by another telecommunications provider, according to Bloomberg reporting published Aug. 19, 2026. The move cut an access path associated with the broader Salt Typhoon espionage campaign targeting telecommunications infrastructure. T-Mobile said in November 2024 that it detected intrusion attempts originating from a connected wireline provider and quickly severed connectivity, while finding no evidence that attackers accessed sensitive customer information, including calls, voicemails or texts. The company also said it could not definitively identify the attacker as Salt Typhoon at the time. U.S. authorities have since attributed extensive telecom compromises to PRC-linked actors, with the FBI reporting activity detected in at least 80 countries and hundreds of U.S. victims. The newly disclosed cable-cutting episode highlights risks created by trusted connections between carriers and other network providers, highlighting concerns about securing critical communications infrastructure.
More context
Timeline
- On September 26, 2024, reports revealed Chinese hackers targeting U.S. internet providers.
- On October 25, 2024, reports identified campaign phones linked to presidential candidates.
- On November 13, 2024, FBI and CISA confirmed telecom network compromises.
- On November 15, 2024, reports identified T-Mobile among campaign targets.
- On November 20, 2024, reports said T-Mobile thwarted deeper attacker access.
- On November 27, 2024, T-Mobile disclosed intrusion attempts through connected wireline infrastructure.
- On November 27, 2024, T-Mobile said customer calls remained inaccessible.
- On December 3, 2024, U.S. officials warned hackers remained inside networks.
- On August 5, 2026, House investigators highlighted dangerous telecom data-center connections.
- On August 19, 2026, Bloomberg disclosed T-Mobile’s physical cable-cutting response.
- On August 20, 2026, coverage emphasized third-party network trust vulnerabilities.
- Over coming months, carriers will likely audit trusted connections aggressively.
- Over coming years, regulators may strengthen telecom cybersecurity oversight requirements.
Why it matters
Immediate US impact: Telecom security concerns intensify across interconnected American communications infrastructure. Possible long-term US impact: Stronger carrier segmentation and third-party cybersecurity controls could become industry priorities. Most affected groups: Telecom carriers, government officials, network operators, customers, regulators, cybersecurity teams. Reader priority: Readers should prioritize primary records, attribution, dates, and independently verified cybersecurity findings.
Coverage notes
Left: Coverage emphasizes systemic vulnerability, regulation, and risks to Americans’ communications privacy. Center: Coverage emphasizes detection, attribution limits, containment, customer-data protection, and network architecture. Right: Evidence insufficient to establish a distinct right-leaning framing pattern.
Primary report
Bloomberg disclosed T-Mobile’s cable-cutting response on August 19, 2026.
Sources
JQJO Editorial Desk · Human reviewed · AI assisted. Report a correction.